Government tightens cyber rules with ban on ransom payments

NewsSupermarkets

The UK government has announced a tough new package of anti-ransomware measures aimed at curbing cybercrime and protecting essential services.

Following public consultation, the Home Office confirmed that public sector organisations and operators of critical infrastructure, such as including hospitals, schools, and councils, will be banned from paying ransom demands.

However, businesses outside this scope will still be required to notify the government before making any such payment, a move that could prevent illegal transfers to sanctioned groups.

The new proposals have drawn strong support across industry, with Co-op CEO Shirine Khoury-Haq, whose business was hit by a cyber-attack earlier this year, welcoming the move.


Subscribe to Grocery Gazette for free

Sign up here to get the latest grocery and food news each morning


“We know first-hand the damage cyber-attacks cause,” Khoury-Haq said. “What matters most is learning, building resilience, and supporting each other to prevent future harm. This is a step in the right direction for building a safer digital future

It is understood that the introduction of mandatory reporting is also being explored by the government, to help law enforcement track threats more effectively.

Speaking earlier this month at the Business and Trade Sub-Committee on Economic Security, Arms and Export Controls, Tuesday, about cyber attack that halted the high street giant’s operations and disrupted business for months, M&S chairman Archie Norman also backed mandatory reporting.

“We do think mandatory reporting is a very interesting idea. It’s apparent to us that quite a large number of serious cyber attacks never get reported to the NCSC,” Norman said, adding, “In fact, we have reason to believe there have been two major attacks of large British companies in the last four months which have gone unreported.”

“I don’t think it would be regulatory overkill to say if you have a material attack, for companies of a certain size, you are required within a time limit to report those to the NCSC, and that would enhance the central intelligence body around this.”

Last month, four were arrested as part of an investigation into the high-profile cyber attacks that severely disrupted operations at M&S, Co-op and Harrods earlier this year.

NewsSupermarkets

Leave a Reply

Your email address will not be published. Required fields are marked *

Fill out this field
Fill out this field
Please enter a valid email address.

NewsSupermarkets

Share:

Government tightens cyber rules with ban on ransom payments
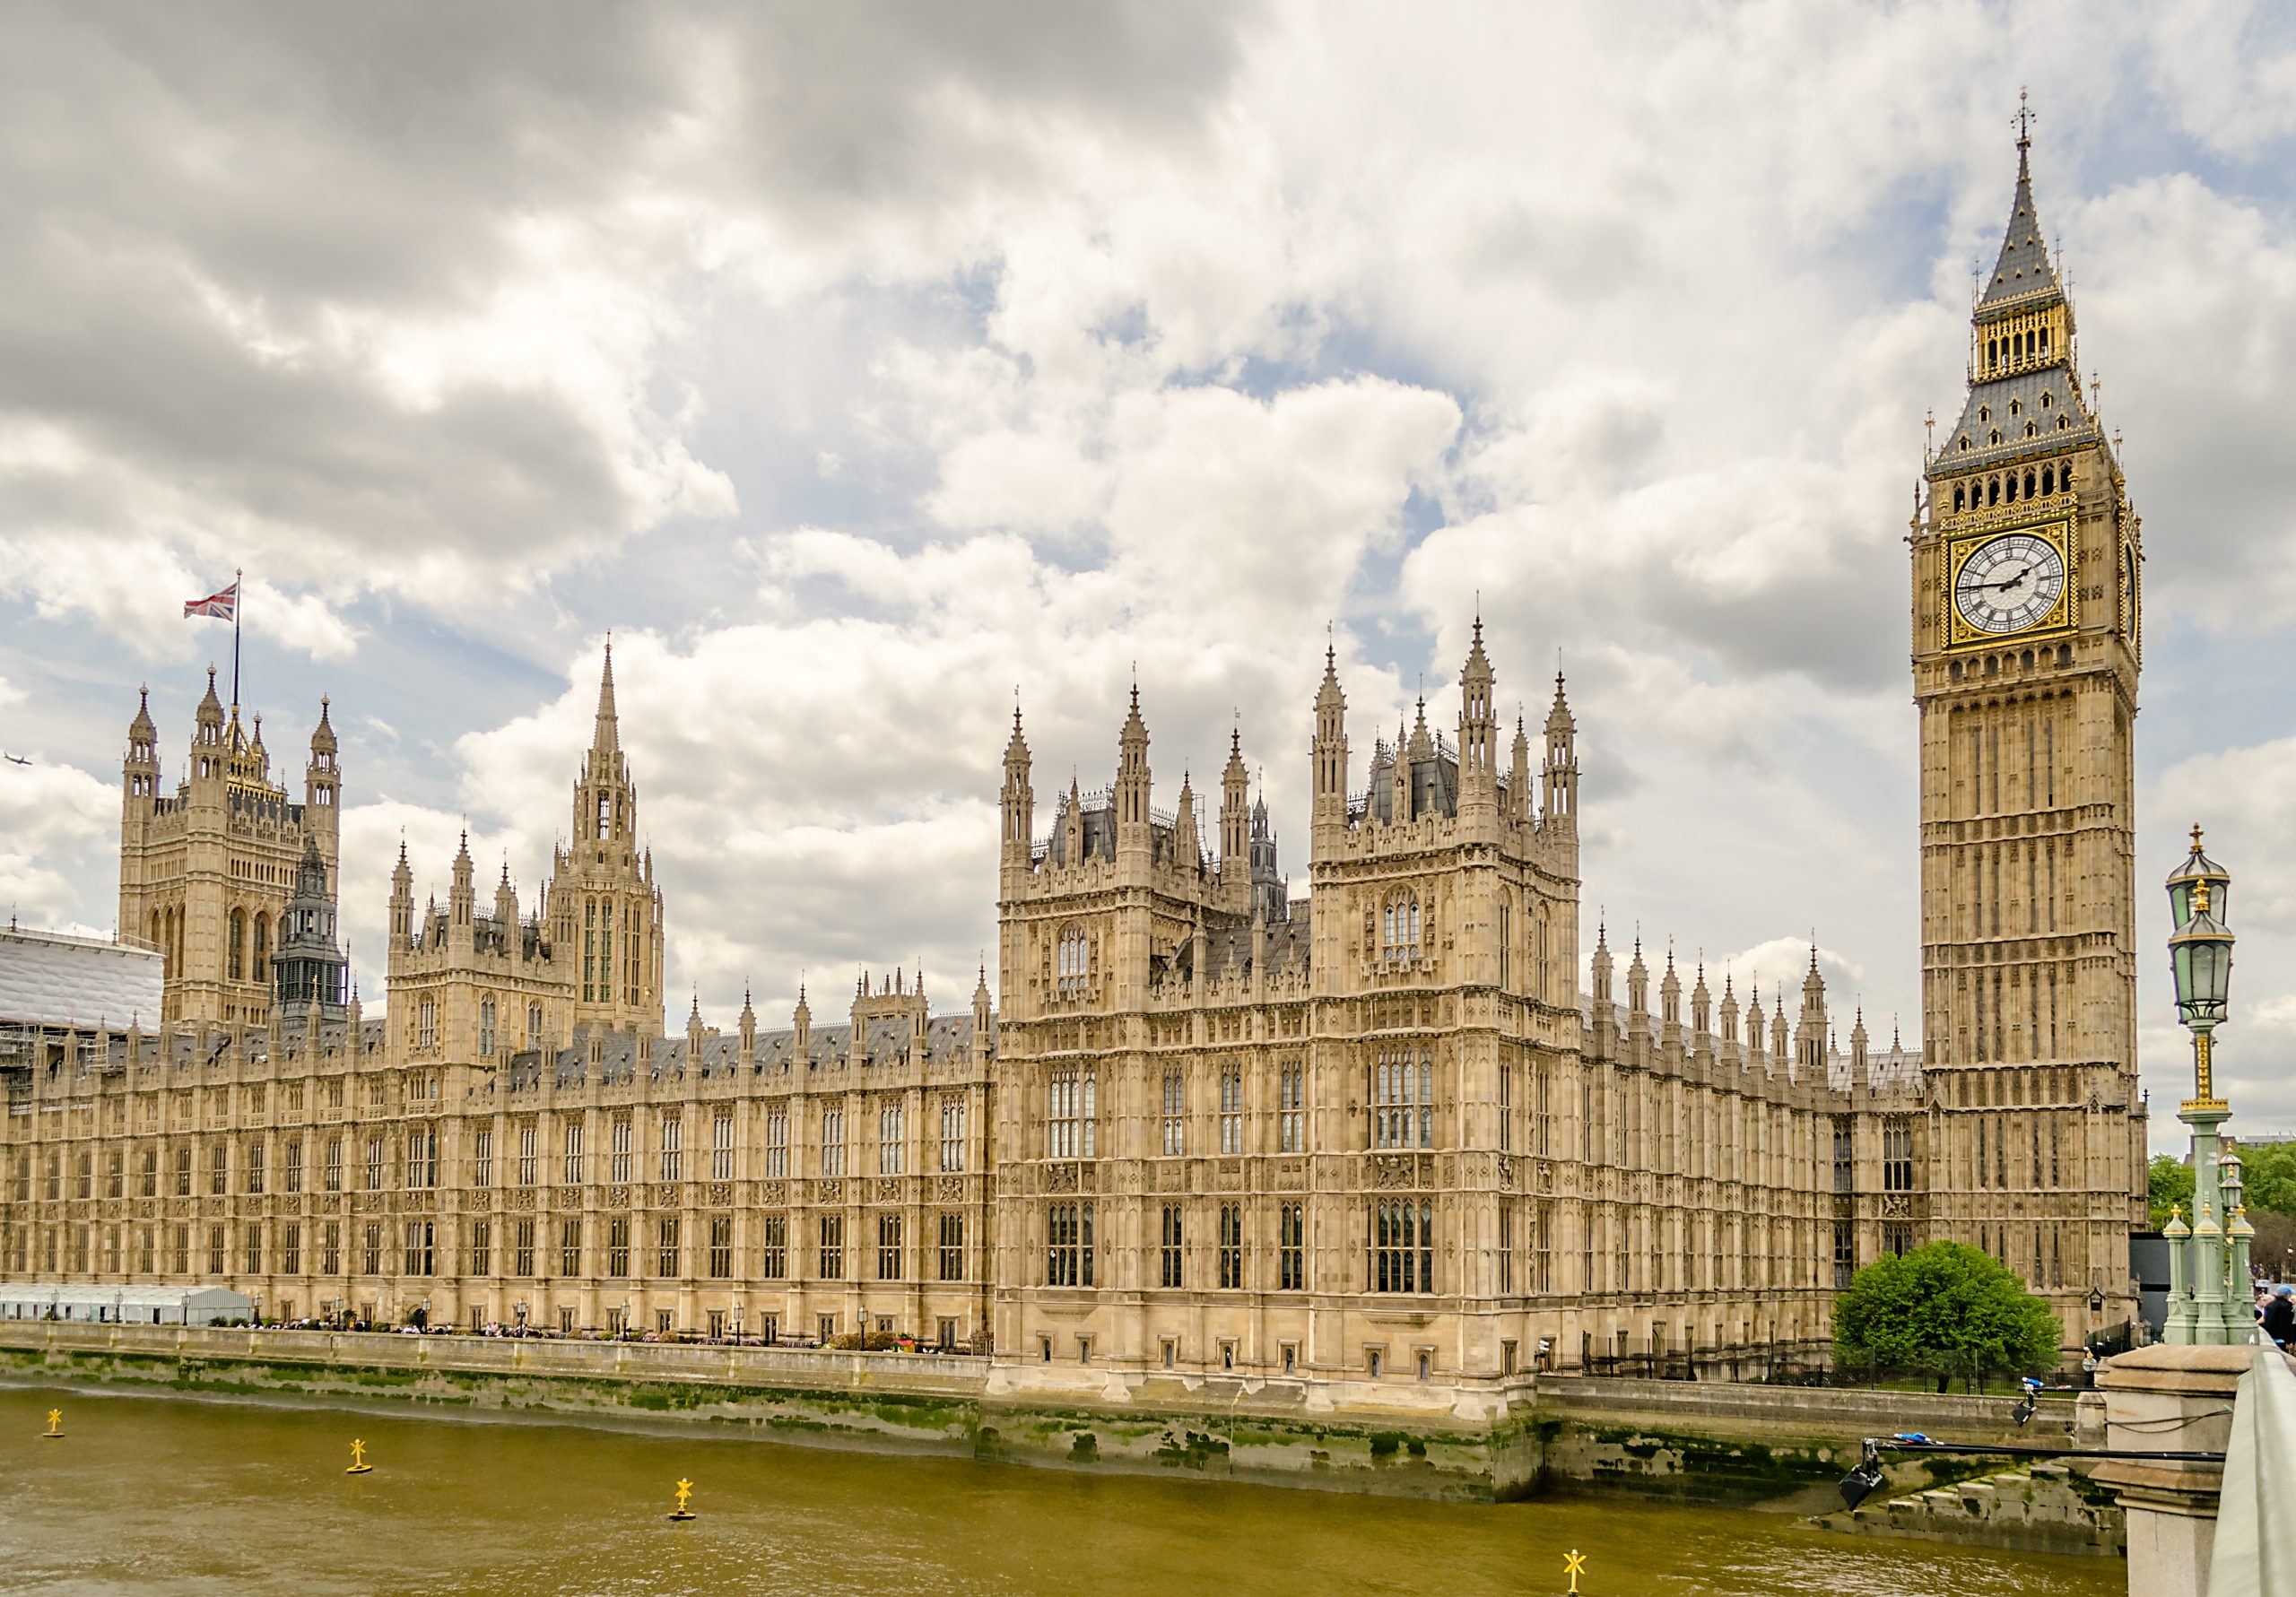
The UK government has announced a tough new package of anti-ransomware measures aimed at curbing cybercrime and protecting essential services.

Following public consultation, the Home Office confirmed that public sector organisations and operators of critical infrastructure, such as including hospitals, schools, and councils, will be banned from paying ransom demands.

However, businesses outside this scope will still be required to notify the government before making any such payment, a move that could prevent illegal transfers to sanctioned groups.

The new proposals have drawn strong support across industry, with Co-op CEO Shirine Khoury-Haq, whose business was hit by a cyber-attack earlier this year, welcoming the move.


Subscribe to Grocery Gazette for free

Sign up here to get the latest grocery and food news each morning


“We know first-hand the damage cyber-attacks cause,” Khoury-Haq said. “What matters most is learning, building resilience, and supporting each other to prevent future harm. This is a step in the right direction for building a safer digital future

It is understood that the introduction of mandatory reporting is also being explored by the government, to help law enforcement track threats more effectively.

Speaking earlier this month at the Business and Trade Sub-Committee on Economic Security, Arms and Export Controls, Tuesday, about cyber attack that halted the high street giant’s operations and disrupted business for months, M&S chairman Archie Norman also backed mandatory reporting.

“We do think mandatory reporting is a very interesting idea. It’s apparent to us that quite a large number of serious cyber attacks never get reported to the NCSC,” Norman said, adding, “In fact, we have reason to believe there have been two major attacks of large British companies in the last four months which have gone unreported.”

“I don’t think it would be regulatory overkill to say if you have a material attack, for companies of a certain size, you are required within a time limit to report those to the NCSC, and that would enhance the central intelligence body around this.”

Last month, four were arrested as part of an investigation into the high-profile cyber attacks that severely disrupted operations at M&S, Co-op and Harrods earlier this year.

NewsSupermarkets

Social

SUBSCRIBE TO OUR DAILY NEWSLETTER

  • This field is for validation purposes and should be left unchanged.

Most Read

Most Read

NewsSupermarkets

Leave a Reply

Your email address will not be published. Required fields are marked *

Fill out this field
Fill out this field
Please enter a valid email address.

RELATED STORIES

Latest Feature

Menu

Please enter the verification code sent to your email: